G01: Specifications, invariants, and finite-state checking
On this page
- Prerequisites and observable goals
- The central question: what must every execution preserve?
- Assertions and Hoare triples
- Worked proof: sum of squares
- Recognition: choose the right evidence
- An inventory transition proof
- Finite exploration and its boundary
- Independent practice
- Smallest useful hints
- Complete solutions: G01
- Retention and readiness
Prerequisites and observable goals#
foundation C01, C04, and C05: state, implications, quantifiers, and induction.
Write a contract, prove a loop’s partial correctness and termination separately, and explain exactly what an exhaustive finite model establishes.
The central question: what must every execution preserve?#
A test is a particular execution. A specification describes permitted executions. An implementation can pass examples while violating an unstated assumption: that inventory never becomes negative, that a rejected transaction has no effect, or that an object remains alive until its last use. Write the objects and the contract before choosing a proof or a test.
For a sequential inventory operation, let the state be , where is available stock and is sold stock. An order requests . Our policy is deliberately simple: accept only when ; otherwise leave state unchanged. The mathematical transition is
This definition contains an error-handling policy, not merely an arithmetic formula. A policy that partially fills orders is also possible, but it is a different operation. The theorem we want is: starting with and nonnegative components, every finite sequence of valid requests preserves and nonnegativity.
Assertions and Hoare triples#
An assertion is a predicate on program state: a statement that can be true or false for a particular mapping from variable names to values. The notation
means partial correctness: for any initial state satisfying , if command terminates normally, its final state satisfies . is the precondition and the postcondition. It does not, by itself, promise termination or describe exceptions. A total-correctness claim adds termination under the precondition. [G-HOARE]
Consider assignment x=x+1 over mathematical integers. To guarantee afterward, it is sufficient to require beforehand, equivalently . This backward substitution is the assignment rule: to establish after , establish before. The substitution replaces the variable’s value in the assertion; it does not execute as a program. With bounded machine integers, overflow behavior must be added to the model. Python’s arbitrary-precision integers avoid fixed-width wraparound, but memory/time remain finite resources.
For a sequence , find an intermediate assertion : prove and . For a conditional, prove each branch under plus its branch condition. Do not prove only the branch you expect to be common.
Worked proof: sum of squares#
Suppose is a fixed nonnegative integer and the program is
i = 0
s = 0
while i < n:
    s = s + i*i
    i = i + 1
An invariant true at every loop head is
An empty sum is zero. Initialization establishes and . For preservation, assume and before the body. The first assignment gives . The second gives , so and . The same assertion is restored, expressed in new state.
At exit, and imply , not merely . Substituting into the sum yields the postcondition . A separate variant is a nonnegative integer at loop heads and strictly decreases on every executed iteration. Thus the loop terminates in the ideal model. An invariant can be true forever in a nonterminating loop; a decreasing well-founded measure supplies the missing argument.
The closed form can be proved by induction, but it is not necessary to prove that the loop computes the specified sum. Keeping the specification as a sum often makes the invariant easier to discover. Prove the closed form separately when it is useful for an oracle or optimization.
Recognition: choose the right evidence#
Use an invariant when the algorithm repeats a step while preserving a relationship. Use structural induction when it traverses a recursively built object. Use a finite-state model when transitions are small enough to enumerate and boundary behavior matters. Use tests to connect that model to the actual implementation. No one method makes the others redundant.
A good invariant is neither only a goal nor only a tautology. “The answer is correct” may be false until completion. “ is an integer” is easy to preserve but too weak to prove the sum. Work backward from the final expression: replace the final bound with the evolving bound , then add bounds needed for safe indexing and exit reasoning.
An inventory transition proof#
For acceptance, implies , and follows from nonnegative inputs. Conservation follows by cancellation:
For rejection, the state is unchanged, so both properties remain true. Induction over the number of requests proves the invariant for every finite sequential request list. This proof is stronger than checking a few orders, but it depends on the transition definition. It does not cover concurrent unsynchronized reads, database failures, or an API allowing a negative request.
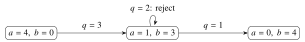
Every shown node sums to four. The self-loop is a real transition: an operation can occur without changing inventory. This matters when distinguishing “no effect” from “no request received.”
Finite exploration and its boundary#
The lab explores all reachable states for a fixed initial stock and request range . Breadth-first search stores a set of seen states so zero requests and rejections do not cause endless repetition. With , every for is reachable by repeatedly ordering one unit. There are states. Each tries requests, so work is transition evaluations, assuming state hashing and integer arithmetic costs are bounded for this model.
The code rejects negative inputs and Booleans, even though Python treats bool as a subclass of int. This is a deliberate contract choice. The exhaustive exploration establishes properties only of this sequential finite model. To model concurrent check-then-decrement, split the operation into read/check/write transitions and include each thread’s local state; the resulting counterexample is not erased by the sequential proof.
Independent practice#
F foundation C standard course work T transfer S optional stretch L runnable lab or project. Attempt the complete set before opening its solutions.
For x=x+3, derive a precondition sufficient to guarantee afterward. State the arithmetic model.
Prove partial correctness of the sum-of-squares loop for , including initialization, preservation, and exit. Then explain why changing the guard to i<=n changes the result.
A proposed proof says “ remains true, therefore the loop terminates.” Refute it with a loop and provide the missing termination condition for the original program.
Two buyers independently check available stock 1, then both record a sale of one before a shared decrement. Construct an interleaving that violates the intended inventory contract. Identify the atomic operation that the sequential model hid.
Change the policy to partially fill an order: sell . Derive the transition and prove conservation/nonnegativity. Explain which previous tests need revision.
Implement reserve and explore in starters/contracts.py. Accept strict nonnegative integers; explore only bounds 0–100. Reject excessive requests without changing state. For , predict all reachable states before executing. Test invalid inputs, zero requests, rejection, and the conservation invariant.
Smallest useful hints#
For .01, replace the post-state by the expression used to compute it. For .04, give each buyer its own read value before choosing the writes. For .06, store seen states before enqueueing successors; do not count a repeated state as new work.
Complete solutions: G01#
Compare the first step where your work differs. A corrected answer is not yet an independent success.
G01.01Show solution
Backward substitution
Use mathematical integers and let be the starting value. After the assignment, . The desired is , then , hence . This is also necessary in this model. Check the boundary: starting at 4 gives 7 and . A fixed-width implementation additionally needs representability of .
Back to G01.01G01.02Show solution
The upper limit follows the guard
Use and . Initialization gives the empty sum. Preservation adds the previously excluded term , then changes the bound to . Exit combines with , giving . With i<=n, an iteration at executes and adds ; the appropriate invariant bound is and final value is . For , the numerical totals happen to agree because , so that single test would miss the specification change.
G01.03Show solution
Safety is not progress
For , i=0; while i<n: pass preserves and never terminates. In the original loop, is an integer bounded below by zero and decreases by one on every iteration. A strictly decreasing sequence in the nonnegative integers cannot be infinite. Decreasing real numbers alone are insufficient: stays positive forever.
G01.04Show solution
The check and effect must agree on one state
Both buyers read and pass the check. If each increments a separately maintained sold total and both overwrite availability with its locally computed zero, the final record can be starting from total one. If they decrement a shared value independently under a different implementation, it may become negative. The exact bad outcome depends on the program; the common defect is that the acceptance decision and inventory change are not one serialized transition. A mutex around the full sequential operation or an appropriate atomic database transaction can enforce that boundary. This is a model-level interleaving, not permission to reason about undefined C++ races as deterministic behavior.
Back to G01.04G01.05Show solution
A different policy, the same invariant
Set and . For nonnegative , , so the new available value is nonnegative; sold is nonnegative because . Their sum is still . A request larger than availability now changes state whenever , so the old excessive-request unchanged-state test is wrong for this new specification. Reuse conservation tests, add the partial-fill acceptance criterion, and do not change tests merely to silence a failure without changing the written contract.
Back to G01.05G01.06Show solution
Complete reference and evidence boundary
The expected states are . The reference follows the mathematical transition, validates the domain before arithmetic, and explores every allowed outgoing transition exactly once per discovered state. The queue may contain several states but never needs to contain duplicates. The code below is complete; the archive’s tests also check through 20 and .
"""G01: a finite state model. This is sequential, not a thread model."""
from collections import deque
from dataclasses import dataclass


@dataclass(frozen=True)
class Stock:
    available: int
    sold: int = 0


def reserve(state: Stock, amount: int) -> Stock:
    if any(type(x) is not int or x < 0
           for x in (state.available, state.sold, amount)):
        raise ValueError("nonnegative mathematical integers required")
    if amount > state.available:
        return state
    return Stock(state.available - amount, state.sold + amount)


def explore(initial: int, max_amount: int = 4) -> set[Stock]:
    if (type(initial) is not int or not 0 <= initial <= 100
            or type(max_amount) is not int or not 0 <= max_amount <= 100):
        raise ValueError("finite model bounds must be integers in [0,100]")
    start = Stock(initial)
    seen, todo = {start}, deque([start])
    while todo:
        state = todo.popleft()
        for amount in range(max_amount + 1):
            nxt = reserve(state, amount)
            if nxt.available < 0 or nxt.available + nxt.sold != initial:
                raise AssertionError((state, amount, nxt))
            if nxt not in seen:
                seen.add(nxt)
                todo.append(nxt)
    return seen


if __name__ == "__main__":
print(sorted(explore(4), key=lambda s: s.sold))Retention and readiness#
Explain why the proof needs both branches, why zero requests do not break exploration, and why this is not a concurrency proof. Revisit implication and induction if those explanations fail. Advance when you can modify the policy, repair the proof, and change tests consistently without viewing the solution. Continue with Hoare logic in Software Foundations for mechanized proof practice; this chapter’s handwritten arguments are not machine-checked proofs. [G-HOARE]